Navigating Canada’s Evolving Cyber Risk Landscape: Key Insights from TECHNATION’s Federal Executive Briefing
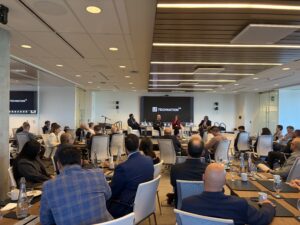
On September 23, TECHNATION’s Federal Executive Briefing: Navigating Today’s Cybersecurity Risk Landscape brought together government and industry leaders for a timely discussion on the rapidly evolving cybersecurity landscape and the strategic choices Canada must make to strengthen national resilience. The conversation explored the growing impact of AI, the widening cyber capability gap, cyber resilience, public-private collaboration, and the role of digital sovereignty in Canada’s future.
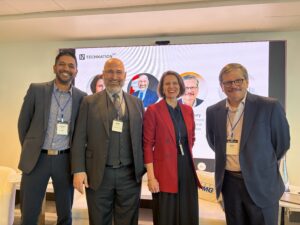 Moderated by Imraan Bashir, Partner and National Public Sector Cyber Leader at KPMG Canada, the discussion featured perspectives from senior government leaders:
- Bridget Walshe, Associate Head, Canadian Centre for Cyber Security
- Nabih Eldebs, Assistant Secretary to the Cabinet, Security and Intelligence Secretariat, Privy Council Office
- Sami Khoury, Former Government of Canada Senior Official for Cyber Security
The conversation reinforced a central reality facing Canada: cyber threats are becoming more sophisticated, more industrialized, and increasingly difficult for any single organization to address alone. As speakers emphasized, cybersecurity is now a leadership challenge that requires collective action across governments, critical infrastructure operators, businesses, and technology providers.
AI is Changing the Balance Between Attackers and Defenders
A key theme throughout the briefing was the growing impact of artificial intelligence on cybersecurity.
 Panelists noted that while AI offers enormous potential to improve detection, automate defensive activities, and increase productivity, it is also reducing barriers for malicious actors. Increasingly accessible AI tools can help attackers operate at greater speed and scale, accelerating an already challenging threat environment. Meanwhile, advances in computing power and the widespread availability of AI capabilities are reshaping long-standing assumptions about who has access to sophisticated cyber tools.
The discussion highlighted a growing concern that AI could widen the gap between organizations with the resources to invest in advanced cyber capabilities and those with limited budgets, talent, and infrastructure. At the same time, panelists stressed that organizations must embrace the same technologies to improve their defences, automate routine security functions, and strengthen resilience.
“Use the threat to defend as well.” – Bridget Walshe
Addressing Canada’s Cyber Capability Gap
Participants discussed what some described as a growing « cyber poverty line, » separating organizations that can afford mature cybersecurity programs from those that cannot.
The conversation explored ways governments and industry can help close this gap through shared services, affordable security tools, knowledge sharing, financial incentives, regulation, and improved access to cyber expertise. Speakers emphasized that improving collective resilience will require raising the baseline level of cybersecurity across the entire ecosystem, not just in the largest organizations.
“We need to make sure that when governments are finding vulnerabilities, when they’re doing testing on AI models, we are also sharing what we are finding as much as possible to the general public, allowing them to defend themselves.” – Nabih Eldebs
From Prevention to Resilience
One of the strongest themes of the discussion was the shift from prevention alone toward resilience.
While prevention remains essential, panelists agreed that organizations must accept that cyber incidents will occur and prepare accordingly. The focus should increasingly be on minimizing disruption, restoring services quickly, and maintaining critical operations during a crisis.
The panel emphasized the importance of tested incident response plans, executive decision-making structures, business continuity planning, and strong relationships between cybersecurity leaders and senior executives. Speakers warned that resilience cannot be reduced to static documentation. It must be actively exercised and embedded in organizational culture.
A recurring message was that organizations should stop asking whether they are completely secure and instead ask how quickly they would know they had been compromised and how quickly they could recover.
“Incidents will happen. The question becomes: how long will it take you to detect what’s happening and how long will it take you to recover?” – Sami Khoury
Building Trust Through Information Sharing
Canada has made progress in fostering greater transparency around cyber incidents while acknowledging that significant barriers remain. Panelists noted that organizations are increasingly willing to disclose cyber incidents and share lessons learned, driven by both regulatory requirements and the practical reality that information sharing benefits the broader ecosystem. Sharing indicators of compromise, tactics, and technical insights can help prevent similar attacks elsewhere and improve national awareness of emerging threats.
Speakers emphasized that stronger trust between government and industry remains essential. Reporting incidents should not be viewed solely through an organizational lens but also as a contribution to Canada’s collective cyber resilience. Several panelists stressed that the relationships needed during a crisis must be established well before an incident occurs.
“None of us can solve cyber alone. Everybody in this room plays a super important role in raising the resilience of Canada.” – Sami Khoury
Digital Sovereignty as a Resilience Imperative
Another important topic was the growing conversation around Canadian digital sovereignty.
Panelists emphasized that sovereignty should not be interpreted as complete digital autonomy. Rather, it is about ensuring Canada retains control over the capabilities and infrastructure required to make critical decisions and maintain essential services.
Key areas identified for increased focus included data sovereignty, digital identity, cryptography, trusted supply chains, and access to domestic technology capabilities. Speakers also stressed the importance of Canadian innovation, research, and cybersecurity expertise as strategic assets that contribute to long-term resilience and competitiveness.
The discussion connected sovereignty directly to resilience, asking what capabilities Canada must retain to continue operating effectively during disruptions, global instability, or cyber incidents affecting critical infrastructure.
“Digital sovereignty does not mean digital autonomy.” – Sami Khoury
Looking Ahead
As the session concluded, panelists urged leaders to strengthen relationships across sectors, test incident response and business continuity plans more frequently, and take practical steps to adopt emerging technologies securely. They also stressed the need for continued investment in cyber talent, collaboration, and national preparedness.
The briefing underscored that cybersecurity is no longer simply an IT issue. It is a strategic challenge that sits at the intersection of national security, public trust, economic resilience, critical infrastructure, and service delivery. Canada’s ability to navigate the next generation of cyber risks will depend not only on technology, but on collaboration, leadership, and collective action.